Understanding Network Threat Detection: A Foundation for Security
In today's digital landscape, the importance of effective network threat detection cannot be overstated, especially for critical infrastructure and industrial security teams. As organizations increasingly rely on interconnected systems, the risk of cyber threats has grown exponentially. This makes it essential for security teams to be equipped with tools and strategies that can effectively identify and neutralize threats before they escalate into significant incidents. This article explores the foundations of network threat detection, its implications for critical infrastructure, and the best practices for a robust security posture.
What is Network Threat Detection?
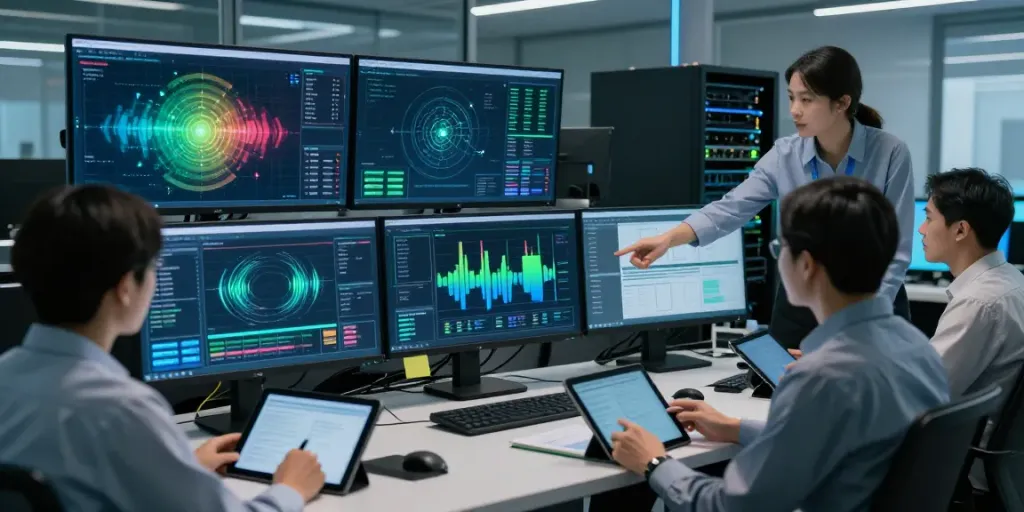
Network threat detection refers to the processes and technologies used to identify malicious or unauthorized activities within a network. This involves analyzing network traffic, system behaviors, and user activities to uncover vulnerabilities that could compromise operational integrity. The ultimate goal is to protect an organization’s assets while ensuring that critical services remain uninterrupted. In essence, it serves as the first line of defense against cyberattacks, providing real-time visibility into the threat landscape.
The Importance of Threat Detection in Critical Infrastructure
Critical infrastructure includes systems that are vital for the functioning of society, such as utilities, transportation, and healthcare services. Any disruption in these services can have catastrophic consequences, ranging from financial losses to public safety risks. Therefore, implementing a robust threat detection system is crucial for safeguarding these infrastructures. Such systems help organizations quickly identify threats and respond effectively, thereby maintaining operational uptime and ensuring compliance with regulatory requirements.
Common Challenges in Implementing Threat Detection Solutions
Despite the importance of network threat detection, organizations often face several challenges in implementation:
- Integration with Legacy Systems: Many critical infrastructures rely on outdated technologies that may not support modern threat detection tools.
- Data Overload: The volume of data generated by operational technology (OT) environments can overwhelm traditional security solutions, making it difficult to pinpoint actual threats.
- Skill Gaps: There is a significant shortage of skilled cybersecurity professionals, which can hinder the successful deployment of threat detection solutions.
- Dynamic Threat Landscape: Cyber threats are constantly evolving, requiring security teams to stay updated with the latest tactics, techniques, and procedures (TTPs).
Key Technologies Behind Network Threat Detection
AI-Powered Tools and Their Role in Cybersecurity
Artificial intelligence (AI) has become a cornerstone of modern cybersecurity strategies, particularly in network threat detection. AI-powered tools analyze vast amounts of network traffic and user behavior in real time, identifying patterns that may indicate security incidents. By leveraging machine learning algorithms, these tools can adapt to new threats autonomously, reducing the time it takes to detect and respond to anomalies. Furthermore, AI enhances predictive capabilities, allowing organizations to preemptively address vulnerabilities before they can be exploited.
Endpoint Monitoring and Its Benefits
Endpoint monitoring is another critical component of effective network threat detection. As devices connected to networks increase, ensuring their security becomes paramount. Endpoint monitoring tools provide insights into the health and security of devices such as servers, workstations, and IoT devices, scanning for unusual activities that may indicate a breach. By monitoring endpoints, organizations can gain a comprehensive view of their security posture and quickly identify compromised systems, allowing for swift remediation actions.
Integrating Threat Intelligence for Enhanced Security
Integrating threat intelligence into network threat detection systems can significantly bolster security measures. This involves the continuous collection and analysis of data about emerging threats from various sources. Organizations can use this intelligence to inform their security strategies, making them more proactive rather than reactive. Threat intelligence not only helps in identifying known threats but also aids in recognizing new attack vectors, enhancing the overall efficacy of threat detection efforts.
Best Practices for Effective Network Threat Detection
Continuous Monitoring: Why It Matters
Continuous monitoring is vital for maintaining an effective network threat detection system. By constantly analyzing network traffic and system behaviors, organizations can detect threats in real time, allowing for immediate response actions. Setting up alerts for suspicious activities and regularly reviewing logs can provide deeper insights into potential vulnerabilities and facilitate quicker threat mitigation. Regular audits and assessments also help ensure that monitoring systems are functioning optimally and adapting to the ever-evolving threat landscape.
Developing a Response Playbook for Threat Remediation
Having a well-defined response playbook is essential in ensuring that organizations can quickly and effectively respond to detected threats. This playbook should outline specific procedures for various types of incidents, detailing the roles and responsibilities of team members during an event. By having a clear plan in place, organizations can minimize confusion during critical moments and reduce their mean time to respond (MTTR), ultimately safeguarding their operational integrity.
Measuring Success: Key Performance Indicators
To assess the effectiveness of network threat detection systems, organizations should establish key performance indicators (KPIs). These can include metrics such as:
- Mean Time to Detect (MTTD): The average time taken to identify a threat after it has occurred.
- Mean Time to Respond (MTTR): The average time taken to respond to a detected threat.
- False Positive Rate: The percentage of alerts that turn out to be non-threatening.
- Incident Recovery Time: The time taken to recover from an incident and restore normal operations.
Regularly reviewing these KPIs enables organizations to refine their strategies and improve their overall security posture.
Emerging Trends in Network Threat Detection for 2026
The Impact of AI and Machine Learning on Threat Detection
As we move deeper into 2026, AI and machine learning are set to play an even more substantial role in network threat detection. Continued advancements in these technologies will enable organizations to achieve higher accuracy rates in threat identification and response. Predictive analytics will allow teams to foresee potential vulnerabilities and address them proactively, while automation will streamline incident response processes. Furthermore, collaborations between AI systems and human analysts will enhance decision-making capabilities.
Cybersecurity Frameworks and Compliance Requirements
The increasing regulatory environment surrounding cybersecurity will require organizations to adopt standardized frameworks for threat detection. Compliance with frameworks such as NIST, ISO, and CIS will not only help organizations meet regulatory obligations but also strengthen their overall security posture. These frameworks provide guidelines for establishing risk management practices, incident response plans, and thorough documentation processes, ensuring organizations remain vigilant against emerging cyber threats.
Future Challenges: Preparing for Evolving Threat Landscapes
As organizations continue to embrace digital transformation, they will face new challenges in network threat detection. The rise of decentralized networks, such as those powered by blockchain technology, presents unique security challenges. Moreover, the proliferation of IoT devices will expand the attack surface, necessitating advanced detection strategies tailored to these environments. Organizations must adopt a forward-thinking approach, continuously updating their threat detection capabilities to adapt to these evolving landscapes.
Frequently Asked Questions about Network Threat Detection
What are the best network threat detection tools?
Some of the best tools for network threat detection include SIEM (Security Information and Event Management) systems, network traffic analysis tools, and endpoint detection and response (EDR) solutions. These tools provide comprehensive monitoring and analysis capabilities, helping organizations maintain a robust security posture.
How does network threat detection fit into cybersecurity strategies?
Network threat detection is a critical component of an organization’s cybersecurity strategy. It not only enhances visibility into potential threats but also enables organizations to respond promptly, minimizing the impact of security incidents. An effective detection strategy promotes a proactive security posture that aligns with overall organizational objectives.
What common misconceptions exist about threat detection?
One common misconception is that threat detection is solely focused on external threats, whereas internal threats can be just as damaging. Another is that automated systems can fully replace human analysts; however, human expertise is still essential for effective incident response and context analysis.
Can AI fully automate network threat detection?
While AI can significantly enhance threat detection capabilities, it may not fully automate the process. Human oversight is necessary for decision-making, particularly in complex situations where nuanced judgment is required. AI systems should be seen as tools that complement human analysts rather than replacements.
How to choose the right threat detection solution for my organization?
Choosing the right threat detection solution involves assessing your organization’s specific needs, budget, and existing infrastructure. Consider factors such as scalability, ease of integration, and the comprehensiveness of monitoring capabilities. Additionally, evaluate vendor support and alignment with industry best practices to ensure a suitable fit.